
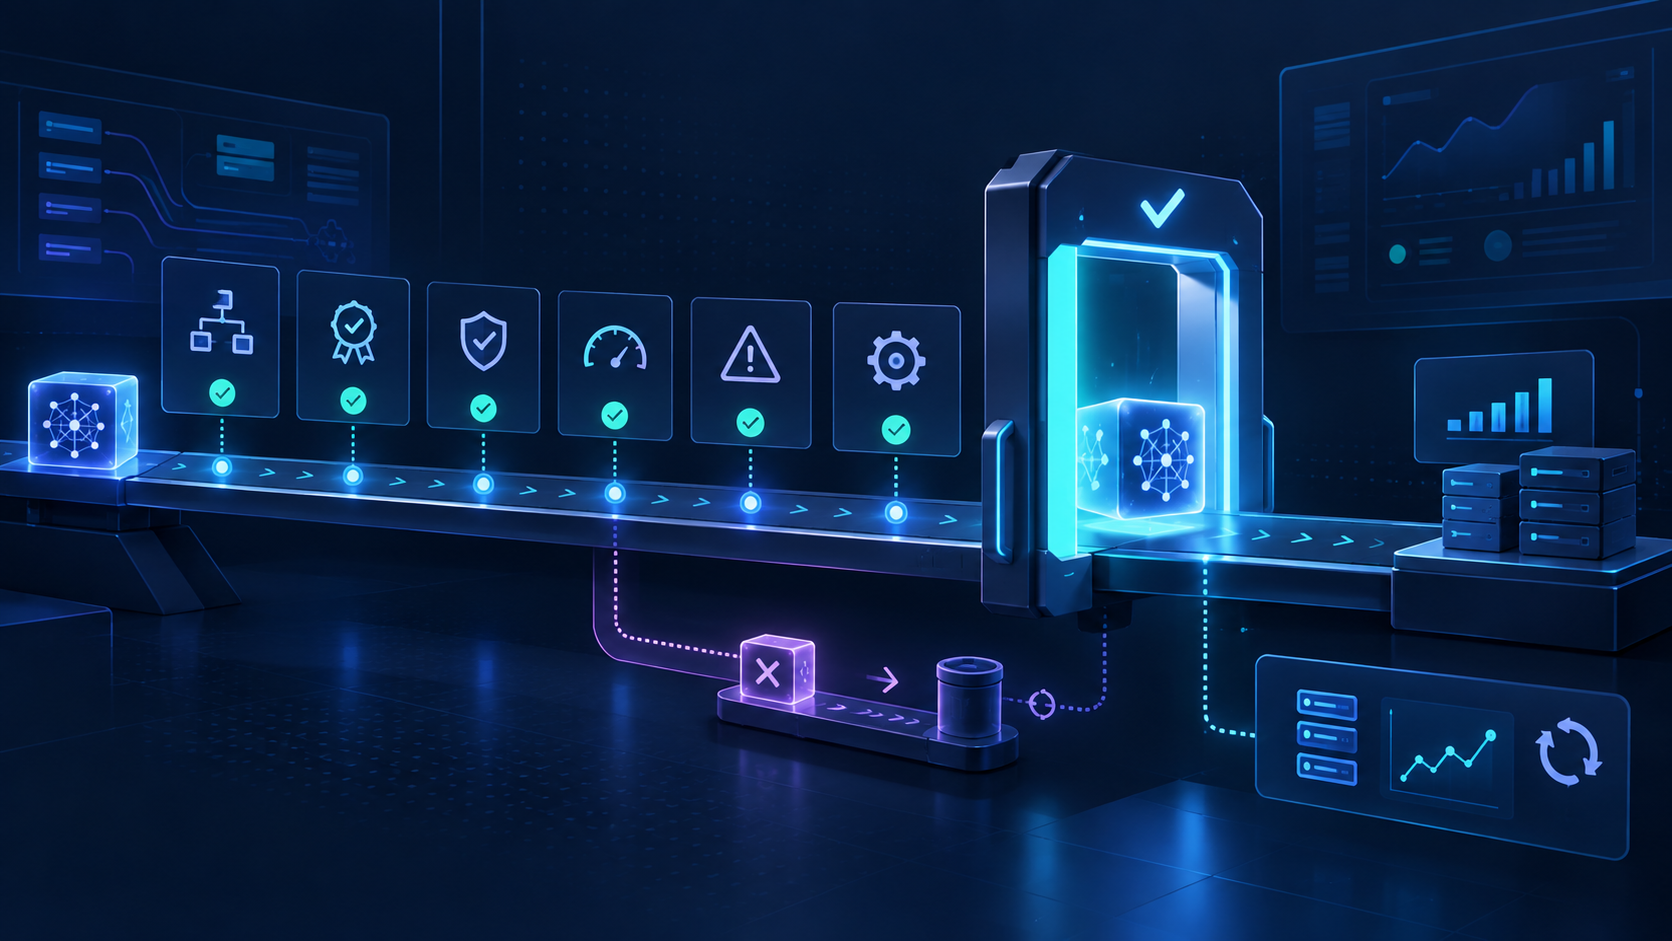
Define AI acceptance criteria through 7 essential checks for workflow fit, factual quality, permissions, latency, cost, failure handling and ownership. This guide explains the decisions, implementation boundaries and review points that matter inside an established product.
Table of Contents
AI acceptance criteria: a practical overview
How to Define Acceptance Criteria for an AI Feature is a practical question for established B2B SaaS teams that already have customers, workflows, APIs, data and permission rules. The useful answer is not a list of model capabilities. It is a way to improve a real product task while keeping the surrounding software understandable, secure and supportable. This guide focuses on the decisions a product and engineering team can make before the feature reaches customers.
AI acceptance criteria need more than expected text
AI features still need clear release standards even though generated behavior is probabilistic. Cover workflow, data, permissions, output quality, failure behavior, latency, cost and operations. Avoid vague phrases such as “the AI should be helpful.” This matters because the decision has to make sense inside the normal product workflow, not only in a demo. The team should be able to explain who benefits, what changes for that user and which existing product boundary remains in control.
Use representative examples and explicit forbidden behavior. Separate deterministic product rules from quality rubrics. In an established product, this affects the API boundary, test cases, support path and what the user sees when something goes wrong. Making that choice explicit early reduces rework and gives product and engineering a shared standard for the first release. The team should be able to test whether the feature is ready rather than debate whether one answer looks good. The practical check is the behavior can be reproduced with representative product data and a real permission context.
Start with workflow acceptance
Define what a real user must be able to do with the feature in the product. Name the roles that can access it. Define the screen or state where it appears. The reason is straightforward: the decision has to make sense inside the normal product workflow, not only in a demo.
State the required input and expected next step. Define what happens when the user accepts, edits or rejects the output. Inside an existing SaaS product, this affects the API boundary, test cases, support path and what the user sees when something goes wrong. A case-summary feature should be judged inside the case workflow, not from a standalone prompt window. A useful test is to ask the behavior can be reproduced with representative product data and a real permission context.
Define data and permission criteria
State which sources the feature may use and which it must never expose. Use server-side tenant and role checks. Include denied-access scenarios in testing. That sounds simple, but the decision has to make sense inside the normal product workflow, not only in a demo.
Define how indexed or derived content inherits access rules. Do not let the model choose whether permission applies. For teams with real customers and production data, this affects the API boundary, test cases, support path and what the user sees when something goes wrong. A cross-tenant retrieval failure is a security defect, not a low AI-quality score. Before moving on, check whether the behavior can be reproduced with representative product data and a real permission context.
Define factual and task quality
Quality criteria should reflect the job the feature performs. For extraction, score field-level accuracy and review flags. For summaries, score critical-fact coverage and unsupported claims. The important point is that the decision has to make sense inside the normal product workflow, not only in a demo.
For recommendations, score policy compliance and evidence use. Separate high-consequence cases from ordinary ones. For a mature SaaS product, this affects the API boundary, test cases, support path and what the user sees when something goes wrong. One average percentage can hide a serious failure in the fields that matter most. A simple way to check this is to ask the behavior can be reproduced with representative product data and a real permission context.
Define source and grounding criteria
When the feature answers from product data or documents, important claims should be traceable. Specify when a source link is required. Test incomplete or contradictory evidence. This matters because the decision has to make sense inside the normal product workflow, not only in a demo.
Define when the feature should ask for review or say it cannot determine the answer. Treat unsupported confident claims as explicit failures. Grounding makes the difference between fluent output and a product answer users can trust.
Define action safety criteria
State-changing features need deterministic acceptance rules around every tool. Define which actions are available. Require server-side authorization and input validation.
Set confirmation policy by consequence. Test duplicate requests, stale state and denied users. The model may propose an action, but the application owns whether it is allowed and executed.
Define latency and availability
The feature needs a response-time expectation that fits the workflow. Set interactive or background timing targets. Define provider timeouts and retries.
Specify the fallback when the AI path is unavailable. Test with production-sized inputs. A thirty-second wait may be acceptable for a background report and unacceptable for an inline suggestion.
Define cost boundaries
Cost is part of the product requirement when usage can scale with customer activity. Measure cost per completed workflow or useful event. Set rate or usage controls where needed.
Compare cost changes with quality changes. Avoid cutting context so aggressively that the feature becomes unreliable. The cheapest model is not a saving if users stop trusting the feature.
Define failure behavior
List the failures the product should handle deliberately. Include missing data, weak retrieval, malformed documents, timeouts and provider errors. Define what the user sees for each class.
Keep the normal product path available when practical. Make review or refusal an accepted outcome when evidence is insufficient. Graceful failure is part of feature quality, not an afterthought.
Define observability and support readiness
The team should be able to investigate customer problems without exposing unnecessary sensitive content. Trace request identifiers, provider choice, retrieval status, tools, latency and errors. Let support identify the feature version.
Capture enough context to reproduce a problem safely. Make product-use signals visible to the owner. A feature is not ready if every support case turns into guesswork.
Example acceptance criteria for an account summary
A concrete example makes the framework easier to use. Authorized users can generate the summary from the account page. All data comes through existing account services.
Risk claims require supporting records. Missing data is omitted or flagged rather than guessed. The user can edit or discard the result, and the team measures latency, cost and correction rate.
Turn criteria into a living test suite
Acceptance criteria should continue protecting the feature after launch. Automate deterministic product checks. Keep representative quality cases versioned.
Add real production failures as regressions. Run the suite when models, prompts, retrieval or tools change. This lets the team improve the AI layer without silently breaking behavior customers already depend on.
AI acceptance criteria: frequently asked questions
Can AI acceptance criteria include percentages?
Yes, when the metric has a clear definition and representative test set. Avoid arbitrary thresholds with no consequence model.
Who should approve the criteria?
Product and engineering should define them together, with security or domain input where the workflow requires it.
How many evaluation examples do we need?
Start with a small representative set covering normal, difficult and high-consequence cases, then add real failures over time.
AI acceptance criteria: final takeaway
How to Define Acceptance Criteria for an AI Feature becomes much easier to plan when the team keeps one real user workflow at the centre of the design. Use the existing product boundaries, make quality measurable and keep the first release narrow enough to understand end to end. That is a more dependable route to production than adding a broad assistant and hoping customers discover the value on their own.
Machine Minds works with established B2B SaaS teams on this kind of bounded AI feature development: shaping the workflow, integrating with real product context, building evaluation and taking the capability through a controlled release. The next step should be based on the evidence from that first feature, not on a generic AI roadmap.
acceptance criteria: further reading and next steps
For a complementary approach to trustworthy AI design, evaluation and ongoing oversight, explore the NIST AI Risk Management Framework. Apply those principles alongside your product’s existing authorization, testing and release controls.
Explore Machine Minds AI Product Engineering and the AI Feature Sprint, or discuss your product workflow with the team.
When planning acceptance criteria, keep the scope tied to one measurable customer task. Review acceptance criteria with engineering and support before expanding the release.
